Surprising fact: a single mis-sent call to a DeFi smart contract can cost as much as a months-long phishing campaign — and that damage often happens before you can hit “cancel.” That counterintuitive reality is why advanced wallets that simulate transactions, expose calldata, and surface contract state are rapidly moving from convenience to core security control for experienced DeFi users in the US and globally.
This article compares two approaches a DeFi user can take when interacting with smart contracts: (A) the minimal, entropy-minimizing path — a simple custody wallet (hardware or hot) with standard UX and limited pre-flight checks; and (B) the proactive simulation-first path — an advanced Web3 wallet that runs transaction simulations, shows precise effects on balances, and enforces safety heuristics. I’ll walk through the mechanisms, where each approach wins or fails, and give a pragmatic decision framework for which to choose depending on activity, tolerance for operational complexity, and threat model.
How smart contract interaction actually works — mechanisms that matter for security
When you “call” a smart contract you submit a signed transaction that includes: destination address, value (ETH), encoded function call (calldata), gas limit & price, and nonce. The EVM executes the contract code deterministically on-chain with whatever state exists at that block. Two points are decisive for security: first, the transaction is irreversible once mined; second, malicious or buggy contracts can do anything allowed by their code and current approvals. That means the relevant protections must occur before you sign — and that’s where simulation fits as a mechanism.
Transaction simulation replays a proposed call against a node (or a forked chain state) without broadcasting it, returning the exact state transitions, events, and final balances if executed now. Good simulators also model slippage, gas consumption, token approvals, and reentrancy effects. Put simply: simulation shows a best-effort “what happens if” under current state. It cannot predict front-running, MEV reordering, or state changes that happen between simulation and mining, but it reduces a large class of human and logic errors upfront.
Limitations matter: simulations depend on the node’s view of mempool and block state, and they often assume the exact same external calls (oracles, flash loans) will behave identically in the live environment. In practice that assumption can fail — especially when interacting with liquidity-sensitive contracts or when gas conditions change rapidly. Still, the information adds strong signal where users previously operated blind.
Two contrasting operational models: minimal custody vs simulation-first
Model A: Minimal custody. You use a standard wallet (maybe hardware, maybe hot), approve tokens through a familiar UI, and rely on visible values (amount in/out, gas fee) plus your own checklist. Strengths: simplicity, fewer opportunities to misconfigure complex options, less cognitive load in fast markets. Weaknesses: approvals are often abstracted away (allowances vs exact approvals), calldata is hidden, and you typically lack a deterministic preview of contract-internal side effects (for example, a contract that sweeps a different token on certain conditions).
Model B: Simulation-first. Before signing, your wallet runs—locally or remotely—a simulation, presents decoded calldata, shows exact post-state balances and traces, and enforces safety checks (e.g., no full-allowance grants without a time or amount cap). Strengths: prevents many logic errors and social-engineering scenarios, makes approvals visible and granular, and produces concrete debugging information when a contract behaves unexpectedly. Weaknesses: heavier UX, potential privacy or latency trade-offs if simulation requires a third-party node, and a false sense of security if users assume simulation guarantees final execution outcomes.
In short: Model A reduces surface area by doing less; Model B reduces surface area by preemptive analysis. Which is better depends on user goals: passive holding vs high-frequency yield harvesting, simple swaps vs complex composable operations involving multiple protocols.
Security trade-offs and attack surfaces
Three threat vectors are especially instructive when comparing approaches.
1) Approval exploitation. Most ERC-20 tokens support “approve” semantics that, when misused, allow contracts to drain large balances. Model A users often grant unlimited allowances for convenience; Model B wallets can parse and flag such calls, insisting on per-amount approvals or automatic allowance revocation. The trade-off: more prompts and transactions to manage allowances versus significantly reduced risk of catastrophic loss.
2) Malicious or buggy contract logic. If a contract contains a hidden sink or a function that behaves different under edge cases, a pre-flight simulation that shows internal traces will reveal suspicious transfers or unexpected state writes. But simulation only sees the current state: if a price oracle update occurs between simulation and mining, the real outcome may diverge. So simulations work best when used with conservative slippage settings, timestamp padding, and by avoiding fragile cross-protocol chains within a single signed transaction.
3) UX-level social engineering. Phishing dapps can craft UI that masks calldata and encourage signing. The decisive defense here is making calldata and approval meanings legible to humans. Wallets that decode function names, parameter types, and token flows force attackers to do harder work; they also shift some responsibility back to the user to recognize anomalies. That shift is beneficial, but only if the wallet’s decoding is accurate and up to date.
Practical comparison: when to pick each approach
If you mainly hold assets and only occasionally swap, Model A (simple custody with hardware keys) may be sufficient provided you follow strict operational hygiene: maintain small hot-wallet balances, use hardware for large holdings, and revoke unused allowances periodically. For active DeFi traders, liquidity providers, or multisig operators the simulation-first model is materially better because the frequency and complexity of interactions multiply exposure to logic bugs and composability risks.
Concretely, choose the simulation-first path when you regularly do any of the following: batch operations across protocols, interact with newly deployed contracts, or receive transaction links from social channels. The extra friction buys clarity: you can see whether a supposed “token swap” actually calls a “sweep” function or whether a strategy contract would change your staking shares.
For US-based users there is an operational nuance: regulatory and tax reporting often requires auditing your own transaction records. Simulation traces and decoded calldata create richer logs for compliance and forensic analysis, reducing time to reconcile odd balances after complex interactions.
How an advanced wallet integrates simulation and safety — a practical checklist
Not all simulation widgets are equal. Useful features to require from a simulation-first wallet include: high-quality calldata decoding (human-readable names), token flow tracing (shows exact token movements), approval management (warns and optionally blocks unlimited approvals), replay on a forked block for deterministic debugging, and local signing with no private-key exposure to remote nodes. A reasonable compromise is to use a wallet that simulates via trusted node providers but performs sensitive checks and decoding locally.
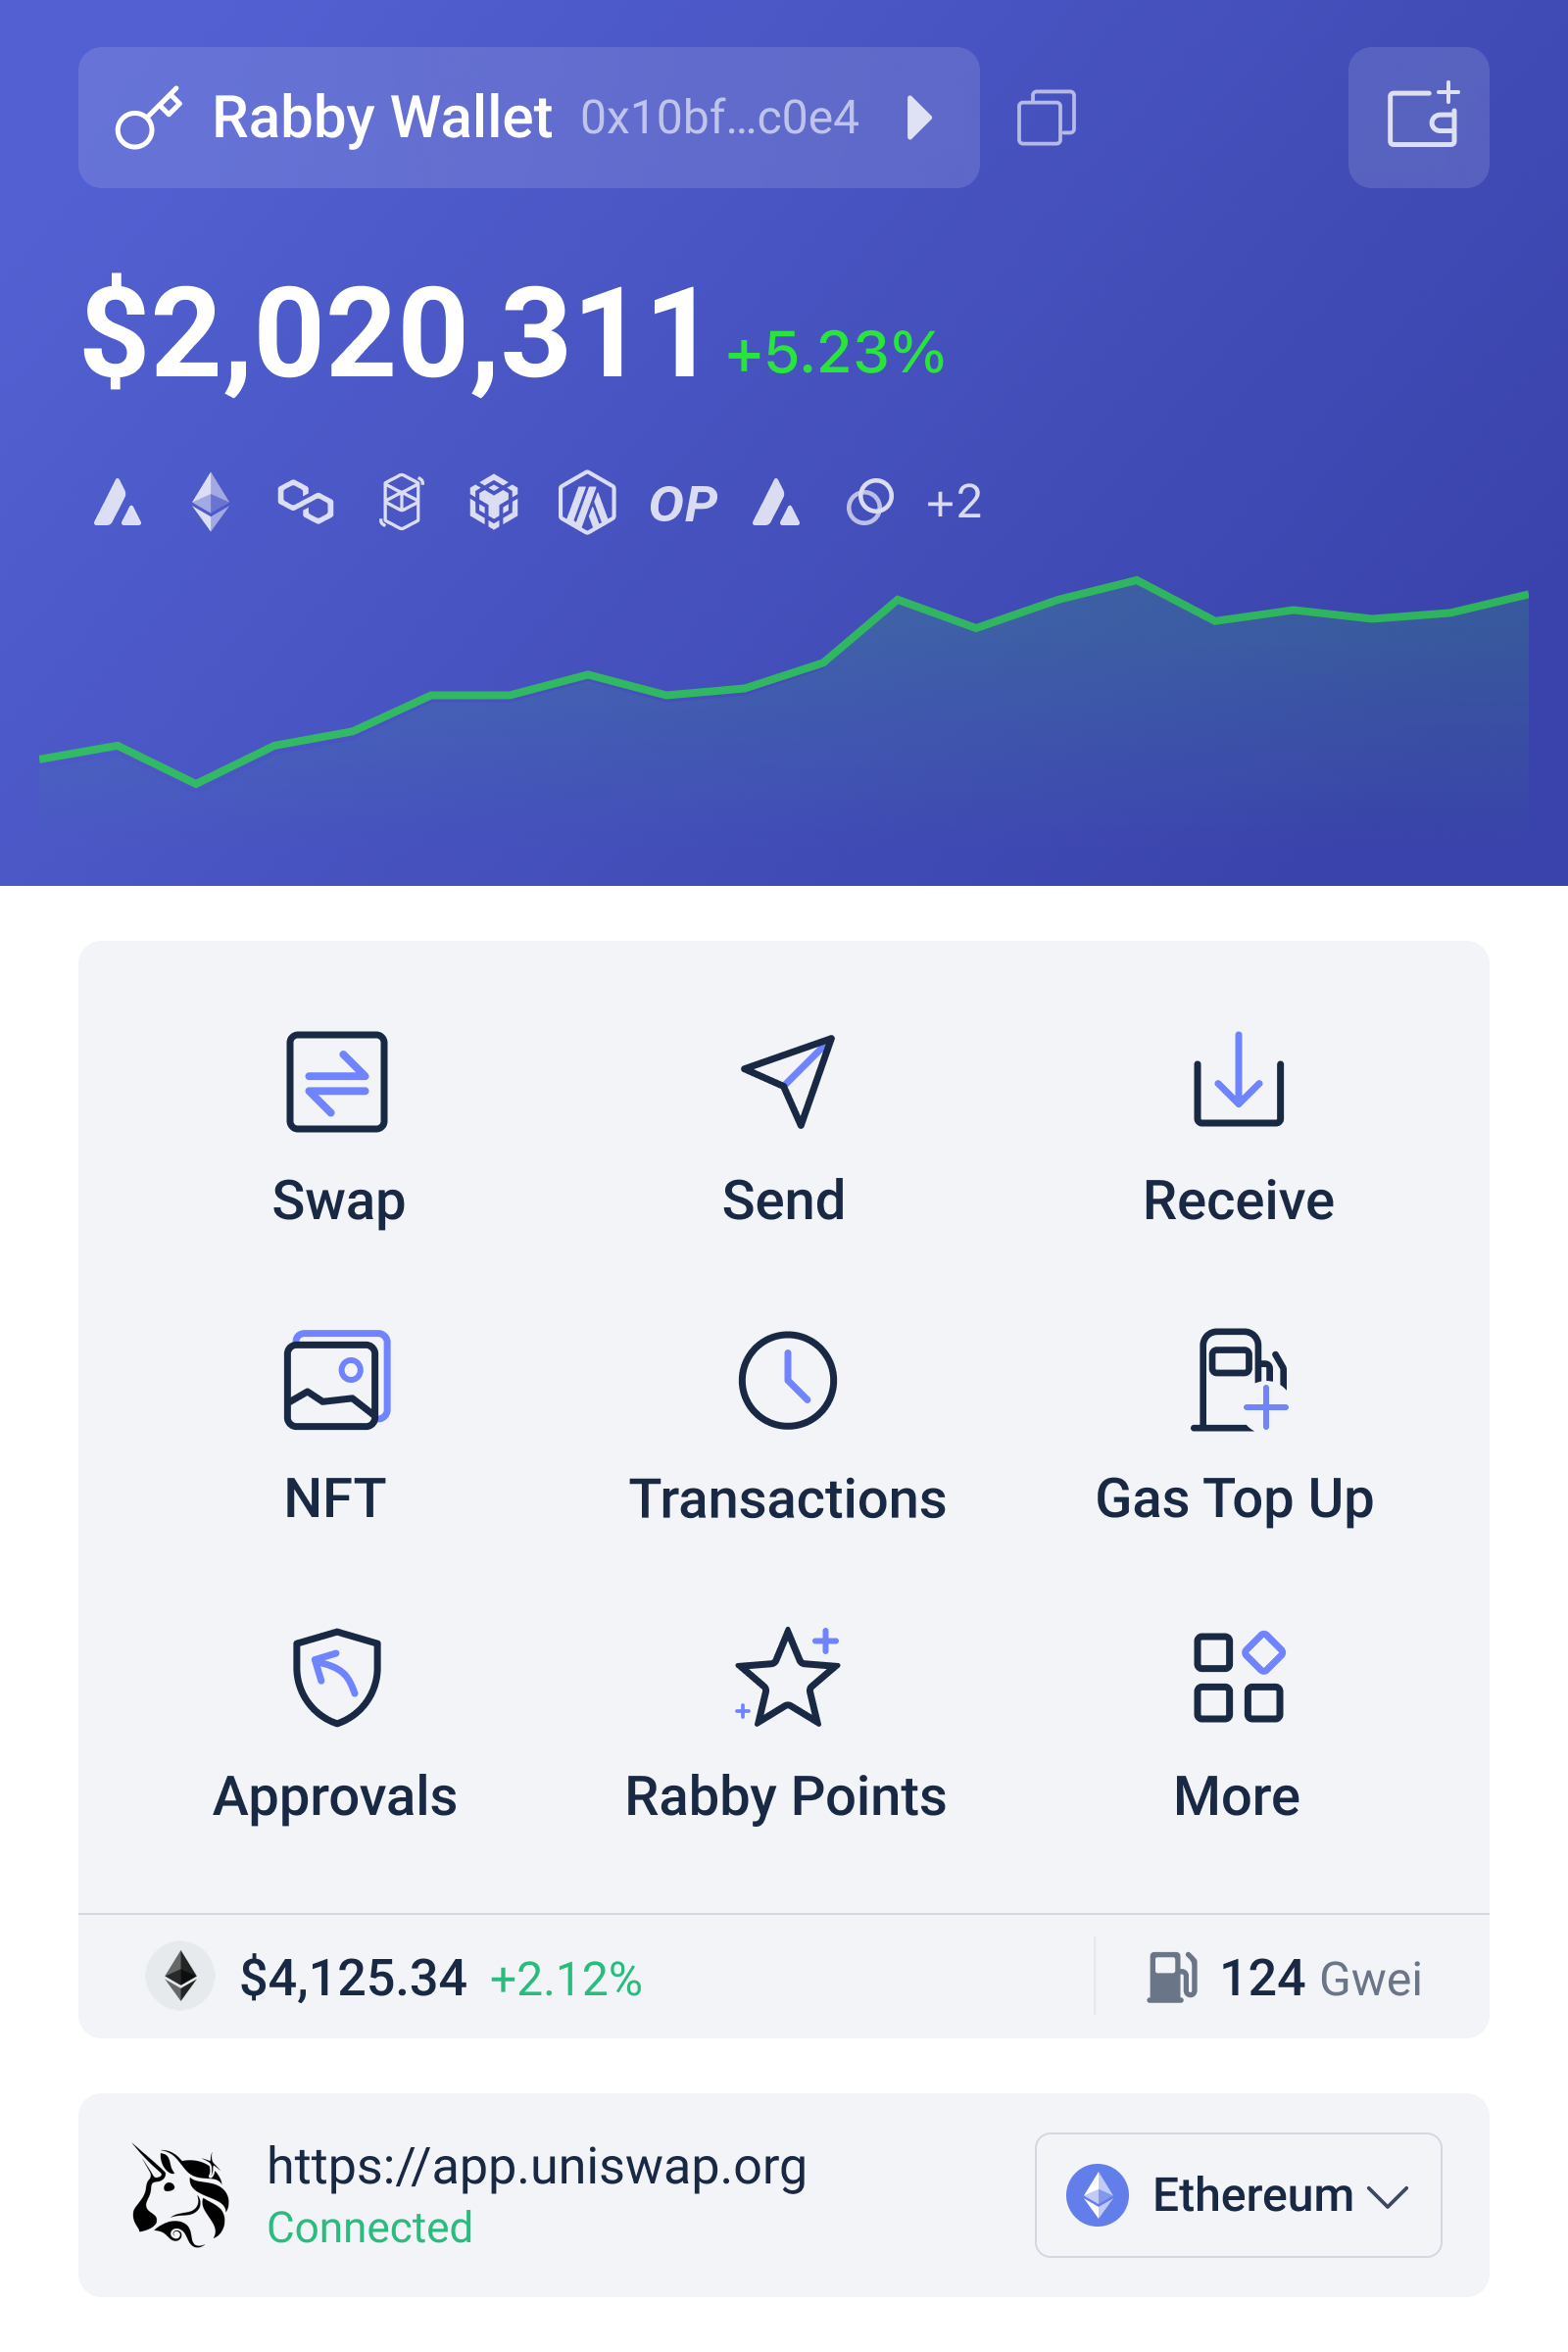
One specific product example that follows this approach is the rabby wallet, which layers simulation and decoded transaction insights into the signing flow. That model demonstrates the core design principle: move as many decisions as possible from intuition to deterministic, inspectable data before any irreversible signature.
Decision framework — a reusable heuristic
Here’s a compact heuristic you can apply in real time: classify each planned interaction by complexity (single-token swap vs multi-protocol batch) and by novelty (well-audited contract vs newly deployed). If complexity × novelty is low, default to minimal workflow; if high, insist on simulation plus allowance restriction and, for very high-risk moves, split actions into smaller steps. This simple multiplier helps allocate cognitive and operational resources where they matter most.
Remember: the simulation reduces but does not eliminate risk. Monitor for time-dependent effects (oracle updates, liquidity shifts), and when in doubt, re-run simulation immediately before signing and consider using gas-fee buffers to reduce the chance of transaction expiration or replacement that alters execution context.
What to watch next — conditional signals and open questions
Watch three signals that will change the balance between the two models: wider availability of private mempool simulation (reduces front-running uncertainty), standardized machine-readable contract metadata (improves automatic decoding), and regulatory guidance that increases the cost of on-chain mistakes (raises the value of auditable pre-flight traces). None of these are guaranteed; each depends on protocol design choices and market incentives.
An unresolved issue is the privacy trade-off: richer simulations are useful, but if they rely on remote nodes they may leak users’ intent to third parties. Expect wallet designs to increasingly offer hybrid modes: local decoding plus optional remote-heavy simulations when the user opts in for deeper analysis.
FAQ
Can a transaction simulation prevent all losses?
No. Simulation is a powerful pre-flight check that reduces human and logic errors, but it cannot prevent losses caused by post-simulation state changes such as oracle price swings, MEV reordering, or front-running. Treat simulation as risk reduction, not risk elimination.
Does simulation require exposing my private key or transaction intent to a third party?
Not necessarily. Good wallet designs run decoding and safety checks locally and only send anonymized calls to remote nodes for execution-time simulation. However, deeper simulations that model mempool or use proprietary heuristics may require interaction with remote services, creating a privacy trade-off you should evaluate.
How should I manage token approvals after using a simulation-first wallet?
Prefer exact-amount approvals where possible, use per-contract limits, and revoke unused allowances regularly. A simulation-first wallet will show approvals before signing and can automate revocation; applying the multiplier heuristic (complexity × novelty) helps decide how aggressively to restrict allowances.
Are simulations accurate for complex multi-protocol transactions?
Simulations can be accurate for complex flows if they run against a precise forked state and include the same external interactions (e.g., oracles). Accuracy degrades when the transaction depends on volatile off-chain inputs or when the simulation cannot replicate concurrent mempool dynamics. Use a conservative approach and split high-risk multi-step flows into smaller transactions where feasible.
Takeaway: for active DeFi users the marginal cost of adding simulation and stronger approval controls to the signing flow is small compared with the asymmetric cost of a single erroneous transaction. Simulation-first wallets do not replace sound operational discipline — they magnify it into deterministic checks that change outcomes. Used thoughtfully, they are a structural improvement in how humans interact with permissionless financial infrastructure.